

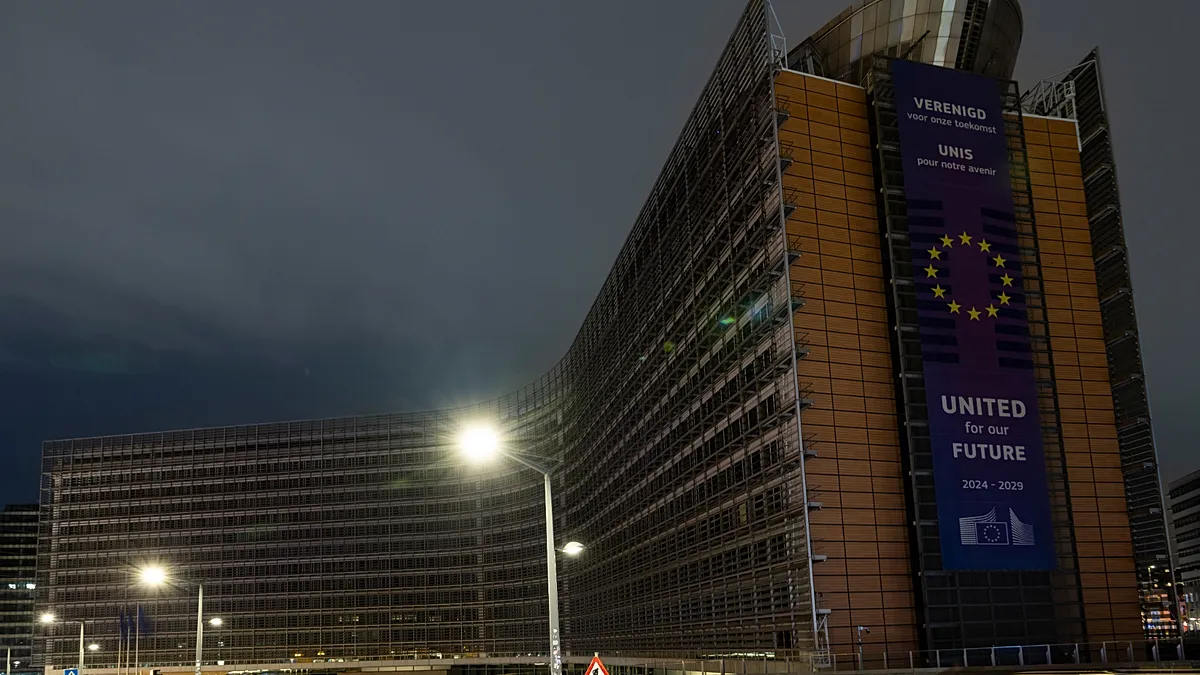
European Commission has suffered a major cyberattack. It is still unclear who is behind it or whether sensitive staff data was stolen. For several days, Commission officials could not log in to Sysper, the internal human resources platform.
There they check salary information, request leave and medical leave, submit timesheets and register for training. The cyberattack on the European Commission has affected these systems, while the investigation continues. On Thursday, Sysper was working again, while the Joint Sickness Insurance Scheme (JSIS) remained out of service, according to an official who spoke to Euronews on condition of anonymity.
Apart from these relatively minor disruptions, most civil servants barely noticed that the systems had been compromised. CERT-EU, the cybersecurity service for EU institutions, is now trying to assess the damage. The main question is whether the attacker, who has not yet been identified, had access to data stored in Sysper, JSIS and other human resources systems.

This would normally not open the way to the Commission’s internal documents, which are stored in a separate system. However, the platforms contain sensitive personal data, including officials’ names, salary grades, home addresses and contact details.
Such a database could feed much more sophisticated campaigns targeting individual staff. EU officials have not yet received official internal communications about the incident, as the extent of the damage is being assessed. The Commission is no stranger to cyberattacks.
In March, its cloud infrastructure hosting the Europa.eu websites was compromised, resulting in the theft of about 91.7 GB of data, including personal information and email content. In January, a cyberattack targeted the Commission’s central mobile device infrastructure, potentially exposing staff names and phone numbers. The Commission did not immediately respond to Euronews’ request for comment.